

Explore our new Cybersecurity Terms Glossary, explained by our experts.

Explore our new Cybersecurity Terms Glossary, explained by our experts.
Cybersecurity Terms Glossary
Multi-account architecture splits a cloud estate into separate accounts or subscriptions so that a compromise, a mistake, or a runaway cost is contained inside one boundary rather than all of them.
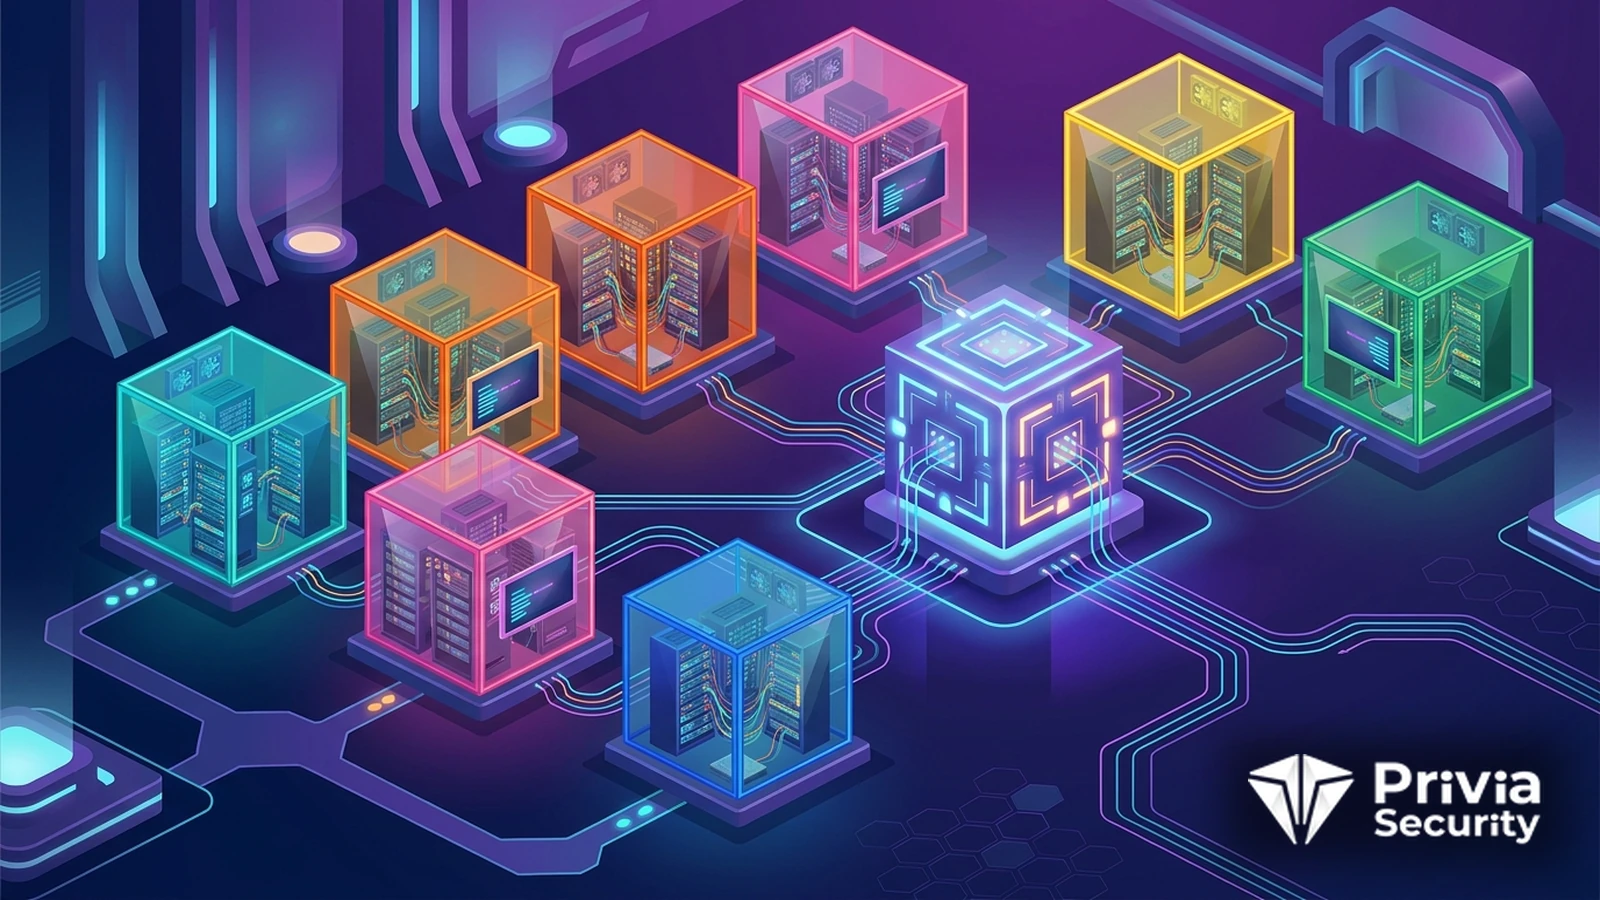
What Is Multi-Account Cloud Architecture?
Multi-account cloud architecture is the practice of dividing a cloud estate into many separate accounts, subscriptions, or projects rather than running everything in one. The account is the strongest boundary any of the major providers offer: identity policies, service quotas, billing, and most blast radius stop at its edge. Splitting along that line means a compromised workload, a deleted resource group, or an accidental public bucket affects one environment instead of the whole business.
A single account starts out simple and ends up as a shared blast radius. Permissions written for a developer in a test environment apply to production resources with the same tag conventions. A CloudTrail configuration change made for one team affects everyone. Service quotas — concurrent Lambda executions, VPCs per region, API rate limits — are consumed collectively, so one noisy pipeline throttles an unrelated application. Most damaging of all, identity sprawl becomes impossible to review: when every role lives in one place, nobody can answer the question of who can reach the customer database.
Separation also makes incident response feasible. Isolating a compromised account by removing its credentials and detaching it from shared networking is a decision you can take in minutes. Isolating a compromised workload inside a monolithic account usually means unpicking dependencies while an attacker is still active.
| Concept | AWS | Microsoft Azure | Google Cloud |
|---|---|---|---|
| Isolation unit | Account | Subscription | Project |
| Grouping | Organisational unit | Management group | Folder |
| Preventive policy | Service control policy | Azure Policy, deny assignment | Organisation policy constraint |
| Landing zone tooling | Control Tower | Cloud Adoption Framework landing zones | Fabric and Terraform blueprints |
Most mature estates converge on a similar shape. A management or organisation root account holds nothing but the organisation itself and is used almost never. Beneath it sit purpose-built accounts: a log archive account that nobody can write to interactively, a security tooling account that holds detection services and read-only roles into everything else, a shared services account for DNS and networking, and then one account per workload per environment. Sandbox accounts for experimentation sit in their own organisational unit with aggressive spending controls and no connectivity to anything that matters.
Preventive policy is what makes the boundary real. Service control policies applied at the organisational unit level can deny the disabling of CloudTrail, block regions you do not operate in, prevent the deletion of log buckets, and stop the creation of IAM users where federated access is the standard. These are guardrails that even an account administrator cannot step over, which is precisely the point — they survive a compromise of that account’s credentials.
Multi-account designs fail in predictable ways, and the failures are usually about the connective tissue rather than the accounts themselves.
root without a condition on the principal or an external ID, turns two accounts back into one. Scope trust policies to specific roles and keep least privilege in the permissions as well as the trust.Auditors appreciate the model because it produces clean evidence: the scope of a PCI DSS assessment can be an account rather than an argument, and separation of duties is demonstrable in the organisation tree. For UK financial entities working under operational resilience expectations, being able to show that an important business service runs in an isolated account with its own identity and logging is a materially easier conversation than describing tags.
Structure is not the same as safety. At Privia Security, we trace real paths between accounts — role chains, shared keys, flat routes — as part of our cloud security services.
There is no correct number; there is a correct rule. Create a new account whenever a workload has a different owner, a different environment, a different compliance scope, or a different availability requirement from its neighbours. Small organisations often run fewer than ten, while large estates run hundreds. The practical limit is how many you can vend and govern automatically, not how many the provider allows.
The accounts themselves are free on all three major providers, and consolidated billing preserves volume discounts and committed-use savings across them. Real costs appear in duplicated shared infrastructure such as NAT gateways, interface endpoints, and per-account tooling licences. Those are usually modest against the containment benefit, and sandbox accounts with hard budget alerts often save more than the structure costs.
No. Tags are metadata that identity policies can reference, but they are set by whoever creates the resource and can be changed, omitted, or mistyped. Tag-based access control is a useful refinement inside an account; it is not a boundary. Service quotas, billing, and most provider-side isolation features operate at the account level and cannot be approximated with labels.
A landing zone is a pre-configured, repeatable baseline into which new accounts are created: the organisational unit structure, identity federation, logging destinations, networking, guardrail policies, and naming standards. Tooling such as AWS Control Tower or the Azure landing zone accelerators automates the setup. The value is consistency, since accounts created outside the pipeline are the ones that later appear in incident reports.
You May Be Interested In These
We use a few cookies that are needed to make this website work, and they are always on. We would also like to set analytics cookies, to see which pages are useful; functional cookies, so that our live chat works; and advertising cookies, to measure our campaigns. We will not set any of those until you say yes, and you can change your mind at any time from the Cookie Settings link in the footer.
Choose the cookies you are happy for us to use. Strictly necessary cookies are always on; everything else is off until you turn it on.
These cookies keep the website working: they hold your security checks, your form submissions and the choice you make here. The site cannot run without them, so they are always on.
These let our live chat open and remember your conversation, and let the newsletter sign-up work. Switch them off and the chat window will not appear.
These tell us which pages are read and how people find us, so that we can improve the site. The reports are about groups of visitors, never about you personally.
These let us measure our advertising and show you our adverts on other websites, such as LinkedIn, Google and Meta. Switch them off and you will still see adverts, but they will be less relevant.


