

Explore our new Cybersecurity Terms Glossary, explained by our experts.

Explore our new Cybersecurity Terms Glossary, explained by our experts.
Cybersecurity Terms Glossary
LoRaWAN security covers the AES-128 key hierarchy, join procedures, and frame counters that protect long-range, low-power sensor networks used in metering, agriculture, and smart cities.
What Is LoRaWAN Security?
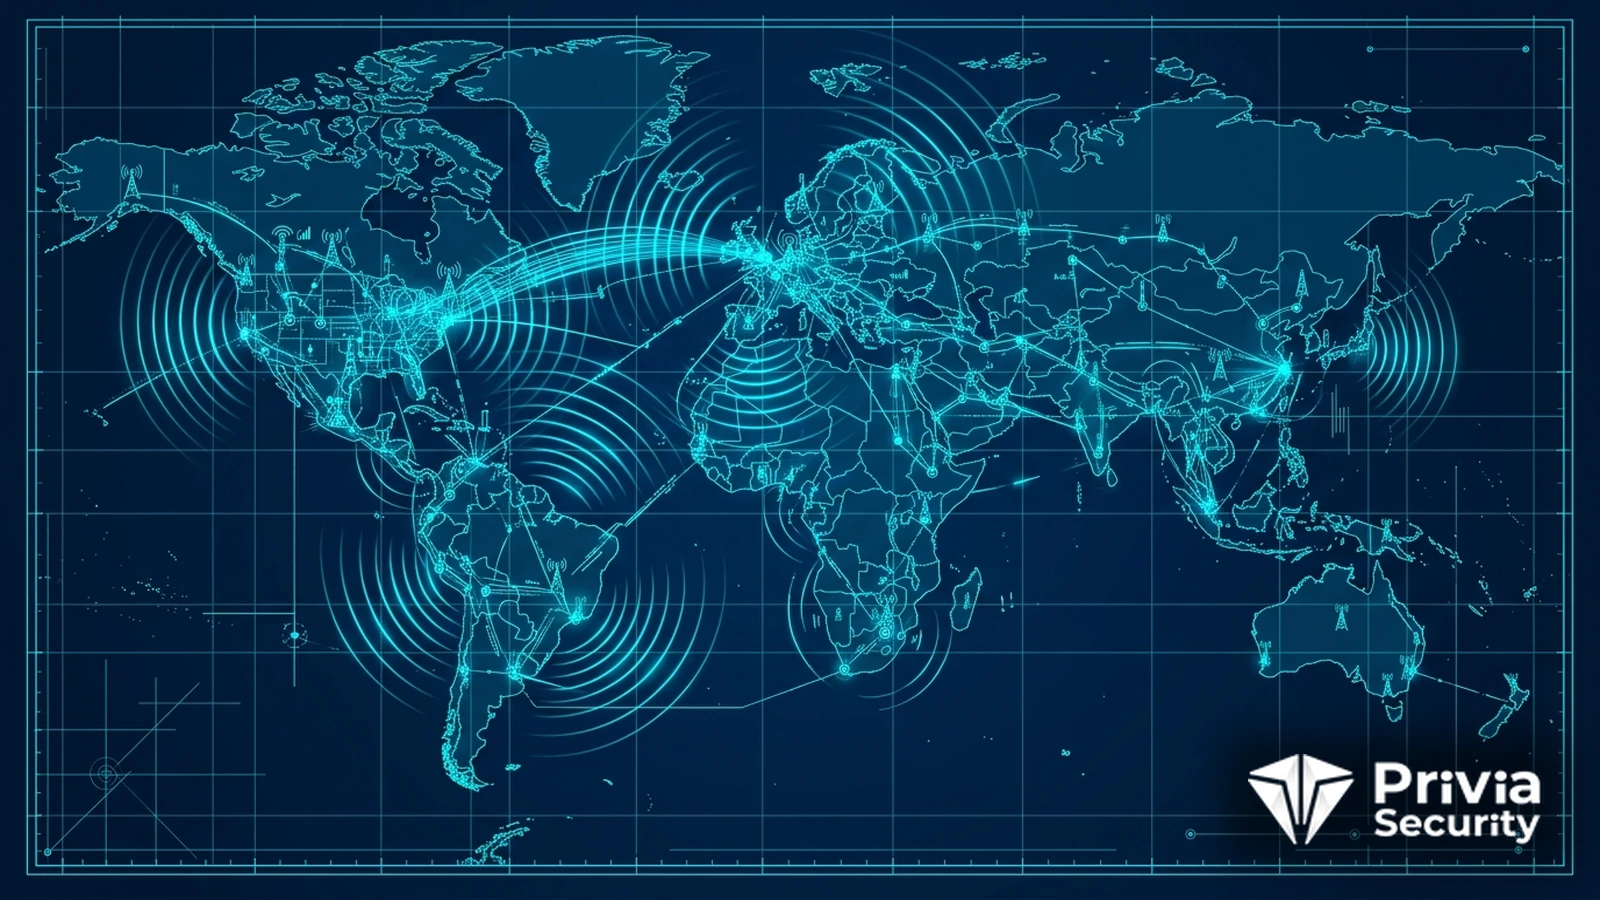
LoRaWAN is the networking layer built on the LoRa radio modulation, designed for devices that send a few bytes occasionally and must run on a battery for a decade. A sensor transmits to any gateway within range — several kilometres in open country, less in a city — and the gateway forwards the packet to a network server over IP. Water meters, soil probes, air quality monitors, parking bays, and building sensors all use it.
Security is built into the specification rather than bolted on, which is unusual in this field. Every payload is encrypted and every frame authenticated with AES-128 from the first version. The difficulties lie in key management, in the gap between specification versions, and in what the network server operator can see.
In LoRaWAN 1.0.x a device holds a single root key, the AppKey. Joining the network derives two session keys from it: the NwkSKey, which authenticates each frame with a message integrity code, and the AppSKey, which encrypts the payload. Because only the application server needs the AppSKey, end-to-end confidentiality from the network operator is possible — provided the keys are actually separated, which in many deployments they are not.
LoRaWAN 1.1, published in October 2017, split the root into a NwkKey and an AppKey held by different parties, introduced a dedicated Join Server, and expanded the network session keys into three with distinct roles for integrity, encryption of MAC commands, and forwarding. It also replaced the random DevNonce with a monotonically increasing counter and added a JoinNonce, closing the replay weaknesses described below.
Over-the-Air Activation has the device perform a join exchange, deriving fresh session keys each time. Activation By Personalisation writes fixed session keys into the device at manufacture and never changes them. ABP is simpler, needs no join traffic, and is a poor idea: the same keys protect every message for the life of the device, and frame counters reset to zero on a power cycle, which opens the door to replay unless the network server handles it carefully. Use OTAA unless something genuinely prevents it.
LoRaWAN runs in the licence-exempt EU868 band in Britain, under the duty cycle limits Ofcom applies to short-range devices. That limit — commonly 1% — caps how often a node may transmit and therefore how quickly it can recover from interference, which belongs in your availability risk assessment. Where the sensors support metering, billing, or regulated infrastructure, the data they carry may also be personal data under UK GDPR, and consumption readings at fine granularity are revealing enough that the ICO’s expectations on minimisation apply.
At Privia Security, our IoT Penetration Test Services assess LoRaWAN nodes, gateways, and the server side together, including key extraction from sample devices.
The payload is encrypted with the application session key, which in principle only the application server holds, so the network operator sees ciphertext. In practice many deployments run both servers on the same platform, so the separation is nominal. If end-to-end confidentiality matters, confirm who holds the application session key and insist on a Join Server arrangement that keeps it apart.
Over-the-Air Activation performs a join exchange that derives fresh session keys, so keys change whenever the device rejoins. Activation By Personalisation hardcodes session keys at provisioning and never rotates them, which makes replay and long-term key compromise far more damaging. OTAA costs a little airtime at join and is the right default for almost every deployment.
For new deployments, specify 1.1-capable devices and servers. For existing estates the upgrade usually means replacing hardware, so it is a refresh decision rather than a patch. In the meantime, mitigate the known 1.0 weaknesses: enforce OTAA, reject frame counter resets, keep a per-device root key, and monitor join traffic for repetition.
Yes. The modulation is resilient to noise but offers no protection against a determined transmitter in the same band, and duty cycle limits restrict how aggressively a node may retry. Treat availability as the weak property: design so that missing data triggers an alert, keep a second communication path for anything safety-related, and avoid using LoRaWAN for time-critical control.
You May Be Interested In These
We use a few cookies that are needed to make this website work, and they are always on. We would also like to set analytics cookies, to see which pages are useful; functional cookies, so that our live chat works; and advertising cookies, to measure our campaigns. We will not set any of those until you say yes, and you can change your mind at any time from the Cookie Settings link in the footer.
Choose the cookies you are happy for us to use. Strictly necessary cookies are always on; everything else is off until you turn it on.
These cookies keep the website working: they hold your security checks, your form submissions and the choice you make here. The site cannot run without them, so they are always on.
These let our live chat open and remember your conversation, and let the newsletter sign-up work. Switch them off and the chat window will not appear.
These tell us which pages are read and how people find us, so that we can improve the site. The reports are about groups of visitors, never about you personally.
These let us measure our advertising and show you our adverts on other websites, such as LinkedIn, Google and Meta. Switch them off and you will still see adverts, but they will be less relevant.


