

Explore our new Cybersecurity Terms Glossary, explained by our experts.

Explore our new Cybersecurity Terms Glossary, explained by our experts.
Cybersecurity Terms Glossary
DLL injection forces a running process to load a library it was never meant to load, so that code executes inside a trusted process with its privileges and identity. It is the best known form of process injection.
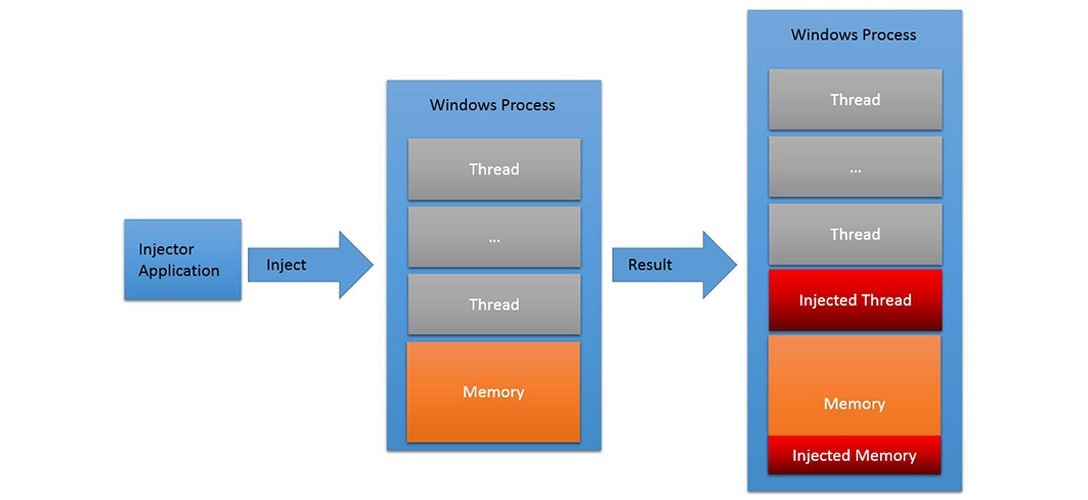
What Is DLL Injection?
DLL injection is a technique for making a running process load a dynamic-link library it was never intended to load, so that the injected code executes inside that process with its identity, its privileges, and its reputation. It is the best known form of process injection and is catalogued by MITRE ATT&CK as T1055.001.
The technique is not malicious in itself. Debuggers, performance monitors, accessibility tools, antivirus products, and game overlays all place code inside other processes. The security problem is that the same mechanism lets malicious code hide inside a trusted process, where its file access and network traffic look entirely ordinary.
Windows processes load libraries at runtime through a documented loader, and a process holding sufficient access rights may open a handle to another process, allocate memory inside it, and begin execution there. Those capabilities exist for legitimate tooling and are governed by access rights rather than forbidden outright. An attacker who has already gained the necessary rights, often through privilege escalation, therefore needs no exploit at all—only the operating system’s own facilities. That places injection firmly in the living off the land category.
Injection leaves traces, provided the telemetry is collected and baselined first—legitimate software is noisy in exactly the same places.
If you find an unexplained module inside a production process, treat the host as potentially compromised and capture memory before anyone reboots it, because reflectively loaded code exists nowhere else. Our incident response services can take the investigation from that point.
You May Be Interested In These
We use a few cookies that are needed to make this website work, and they are always on. We would also like to set analytics cookies, to see which pages are useful; functional cookies, so that our live chat works; and advertising cookies, to measure our campaigns. We will not set any of those until you say yes, and you can change your mind at any time from the Cookie Settings link in the footer.
Choose the cookies you are happy for us to use. Strictly necessary cookies are always on; everything else is off until you turn it on.
These cookies keep the website working: they hold your security checks, your form submissions and the choice you make here. The site cannot run without them, so they are always on.
These let our live chat open and remember your conversation, and let the newsletter sign-up work. Switch them off and the chat window will not appear.
These tell us which pages are read and how people find us, so that we can improve the site. The reports are about groups of visitors, never about you personally.
These let us measure our advertising and show you our adverts on other websites, such as LinkedIn, Google and Meta. Switch them off and you will still see adverts, but they will be less relevant.


