

Explore our new Cybersecurity Terms Glossary, explained by our experts.

Explore our new Cybersecurity Terms Glossary, explained by our experts.
Cybersecurity Terms Glossary
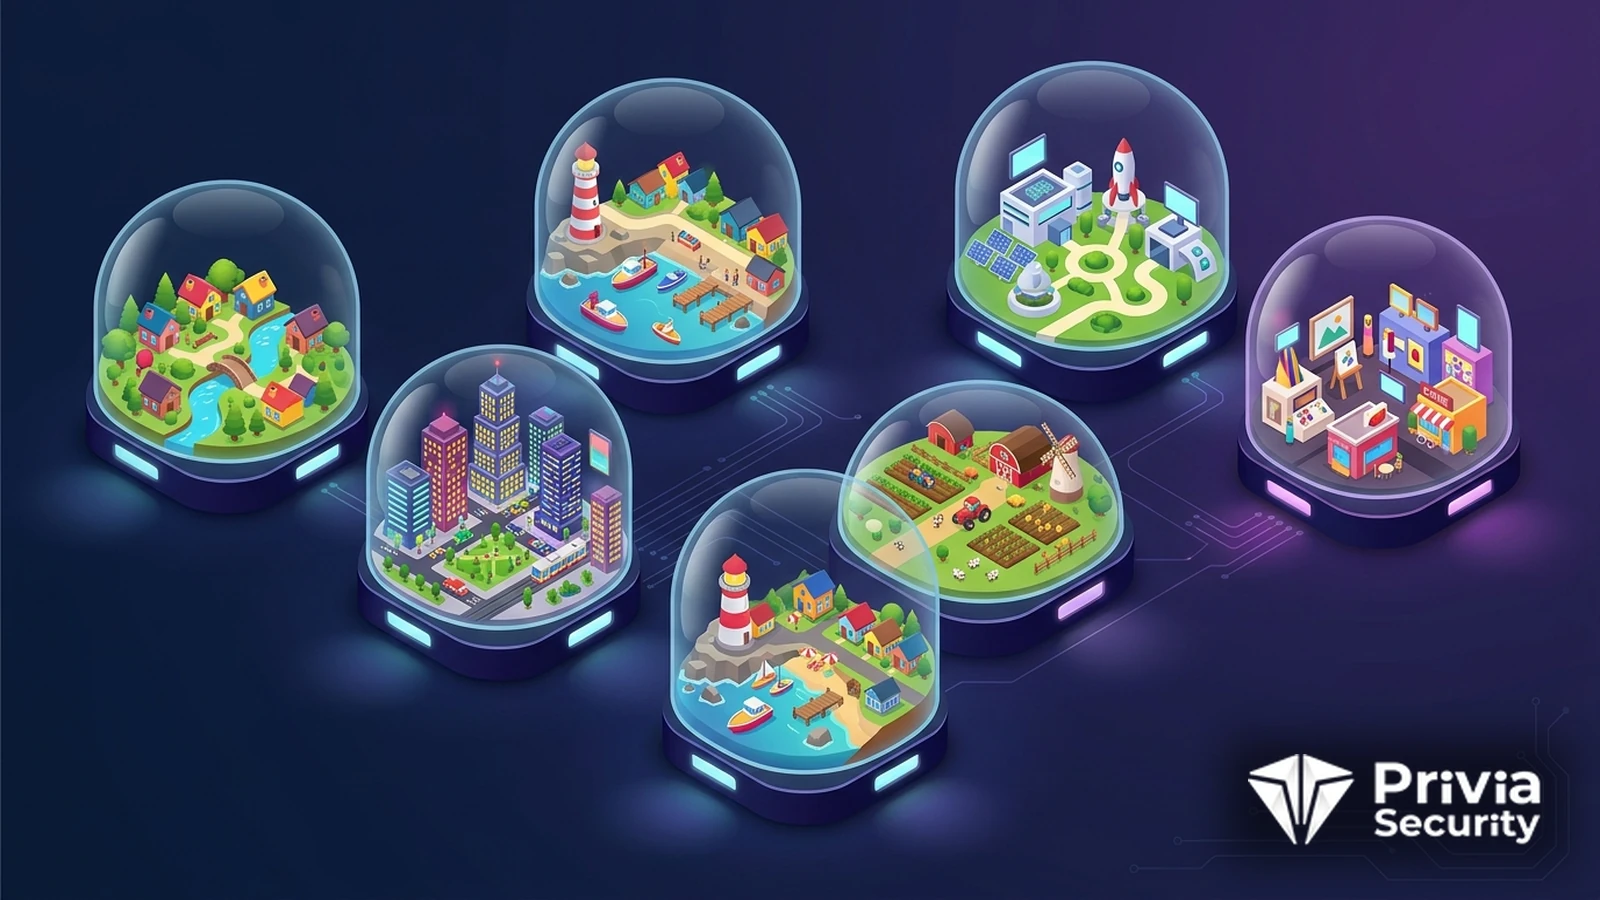
A mobile app sandbox confines each application to its own files, memory, and limited set of system calls, so a compromised app cannot read the data of the apps beside it.
What Is a Mobile App Sandbox?
Put fifty apps on one phone and you have fifty separate trust decisions sharing a single device. The sandbox is what keeps them apart: each app gets its own storage, its own process boundary, and a restricted view of the system, so a dating app cannot read your banking session and a compromised game cannot harvest your messages.
This is the same idea as sandboxing elsewhere in security, but with one difference that shapes everything else. On a phone it is not optional and not a research feature—it is the default execution model for all third-party code, applied from the first install.
Android reuses Linux primitives it already had. At installation each app receives a unique user ID, and the files in its data directory are owned by that UID, so ordinary filesystem permissions do most of the work. SELinux, enforcing for every domain since Android 5.0, adds mandatory access control on top: policy, not file ownership, decides which domains may talk to which sockets, devices, and services. Seccomp filters then shrink the set of system calls an app can reach at all.
Communication crosses the boundary only through channels the kernel mediates—Binder IPC, intents, content providers, and shared storage. Scoped storage, enforced from Android 11, closed the oldest hole by removing broad read access to the shared partition, so an app sees the media it created and nothing more.
Apple applies a sandbox profile to every process, including its own daemons. Each app lives in a randomly named container directory, cannot enumerate other containers, and reaches system services through XPC. Capabilities beyond the default profile arrive as entitlements signed into the binary, so an app cannot grant itself access to, say, the Keychain sharing group of another vendor. App groups provide the deliberate exception, letting apps from the same developer share a container.
Most sandbox failures in practice are developer mistakes rather than kernel bugs.
Genuine escapes exist too, and they are serious. CVE-2019-2215, a use-after-free in Android’s Binder driver, was exploited in the wild as part of an attack chain. On iOS, FORCEDENTRY (CVE-2021-30860) broke out of the iMessage parsing context to deliver Pegasus with no user interaction—the reason Apple built the BlastDoor service. Both show the standard pattern: the sandbox rarely falls alone, it falls as the second or third link in a chain.
On a rooted or jailbroken handset, the guarantees thin out. Code running with system privileges can read any container, so an app that trusted the sandbox to keep its database private no longer has that assurance. This is why high-value apps combine sandbox-aware storage with root and jailbreak detection, and why sensitive material belongs in hardware-backed stores—the Android Keystore or the iOS Keychain with a device-only accessibility class—rather than in a file the sandbox happens to protect today.
A competent mobile assessment treats the sandbox as something to probe rather than assume. Testers enumerate exported components and launch them from an unprivileged app, inspect the container for plaintext secrets, drive the app through deep links with hostile parameters, and check whether backups or task snapshots carry data outside the boundary. OWASP MASVS places these checks under the platform and storage groups, as described in our guide to MASVS and MASTG.
At Privia Security, our Mobile Application Security Services test exactly these boundaries on both platforms, on rooted and unmodified devices.
Yes, through supported mechanisms. On iOS, app groups give apps signed by the same team a shared container and shared Keychain access. On Android, apps signed with the same key can declare a shared user ID on older API levels, though the feature is deprecated, and the modern approach is an explicit content provider or account authority with permissions attached.
Partly. The sandbox is an operating system control, so it holds while the system is running normally, and full-device encryption protects data at rest while locked. An unlocked device, or one with an unlocked bootloader or jailbreak, exposes container contents to anyone with physical access. Store secrets in the Keystore or Keychain with a device-only, unlock-required class instead.
Because they are doors you opened yourself. An exported activity, service, broadcast receiver, or content provider with no permission requirement can be invoked by any other installed app, including malware. If that component writes files, returns data, or performs a privileged action, the isolation guarantee is gone. Export only what genuinely needs cross-app access, and protect it with a signature-level permission.
Rare, expensive, and usually part of a chain. Commercial spyware vendors buy them, and both Apple and Google treat them as critical. For most organisations the realistic risk is not a kernel escape but an app that leaks data through its own exported components, shared storage, or logs, which is where assessment effort pays off.
You May Be Interested In These
We use a few cookies that are needed to make this website work, and they are always on. We would also like to set analytics cookies, to see which pages are useful; functional cookies, so that our live chat works; and advertising cookies, to measure our campaigns. We will not set any of those until you say yes, and you can change your mind at any time from the Cookie Settings link in the footer.
Choose the cookies you are happy for us to use. Strictly necessary cookies are always on; everything else is off until you turn it on.
These cookies keep the website working: they hold your security checks, your form submissions and the choice you make here. The site cannot run without them, so they are always on.
These let our live chat open and remember your conversation, and let the newsletter sign-up work. Switch them off and the chat window will not appear.
These tell us which pages are read and how people find us, so that we can improve the site. The reports are about groups of visitors, never about you personally.
These let us measure our advertising and show you our adverts on other websites, such as LinkedIn, Google and Meta. Switch them off and you will still see adverts, but they will be less relevant.


